FYB Connect 365|2CM Azure App Registration
OVERVIEW
To use 365|2CM you are required to register the application on Azure Active Directory. The registration will be used to acquire an access token to make web API requests to access certain Microsoft resources for a tenant (organisation).
APP REGISTRATION USING THE WEB PORTAL
-
Sign in to Azure web portal using the link below https://azure.microsoft.com/en-gb/features/azure-portal/
-
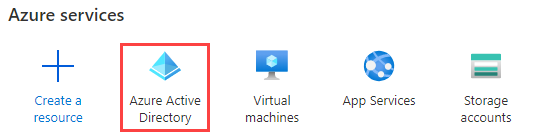
Once signed in, click on the Azure Active Directory button
-
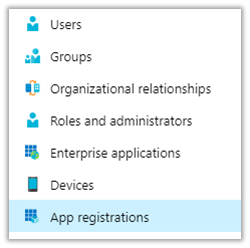
Click on the App Registrations option from the left menu
-
Click on the New registration button

-
Enter 365|2CM into the name input field

-
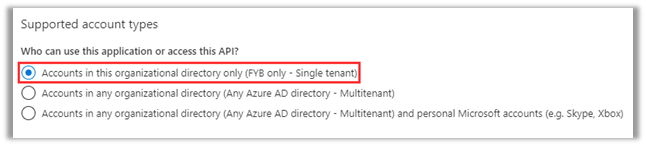
Under Supported account types section enabled Accounts in this organizational directory option
-
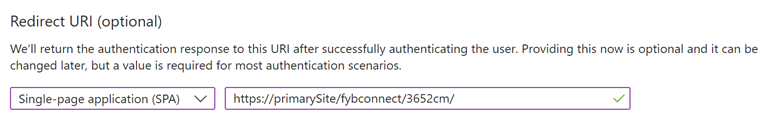
Select Single-page application (SPA) from the drop-down menu and type in the hostname configured for FYB Connect followed by /3652cm/
NoteThe URI is case sensitive, the route must match exactly the pattern below where the only variable that needs to be replaced is the hostname. Please include the trailing slash in the URL and ensure all characters are in lowercase. Example: https://hostname/fybconnect/3652cm/
-
Click on the Register button
GRANTING API PERMISSION
The application will require various API permissions, please follow the steps below to add the required permission for 365|2CM.
-
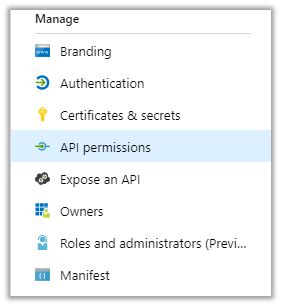
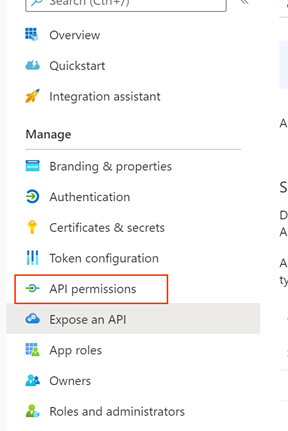
Click on the API permissions option from the left menu
-
Click on the Add Permissions button

-
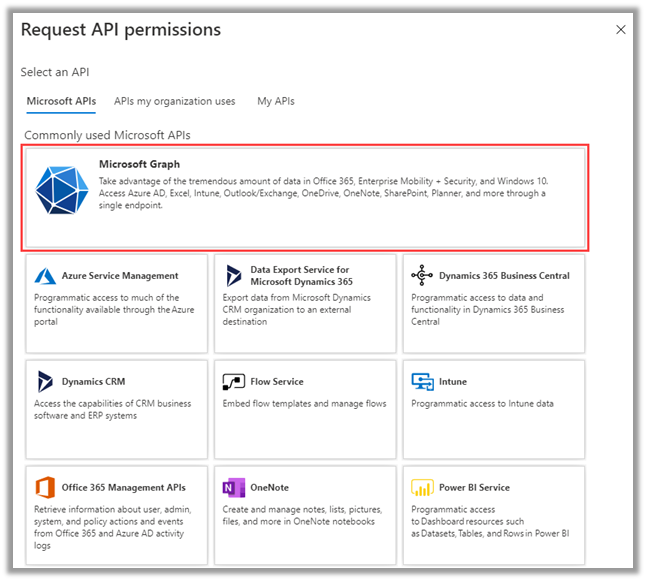
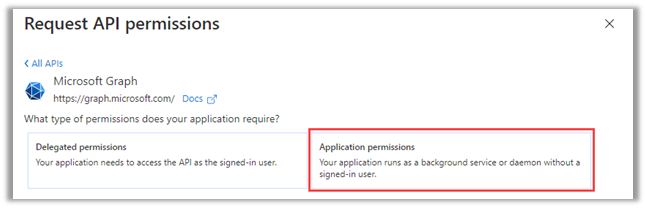
When the right-hand permission panel appears, click on Microsoft Graph (This will be at the very top)
-
Click on Application permissions
-
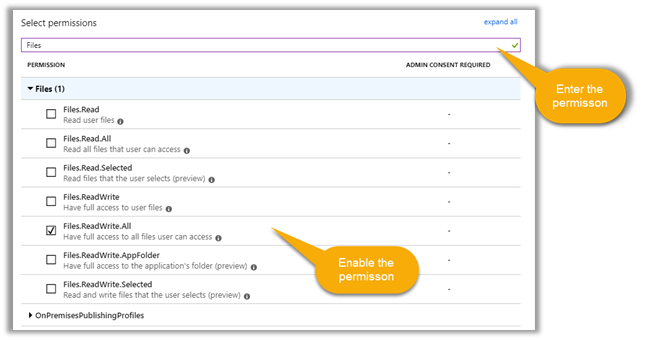
Using the select permission window, add the following permissions to the application
-
Files.ReadWrite.All
-
Sites.Read.All
-
Scroll down to the bottom of the panel and click the Add Permission button

-
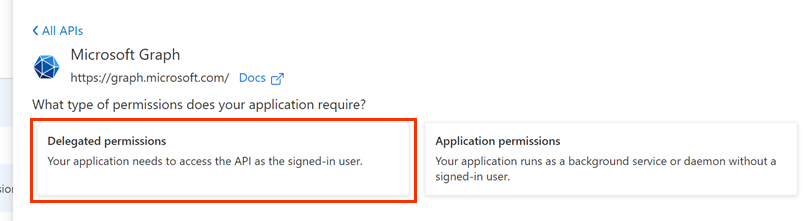
Go back and repeat Steps 2 and 3 except this time select Delegate permissions
-
Using the select permissions window and add the following delegate permissions to the application
- Channel.ReadBasic.All
- ChannelMessage.Read.All
- Chat.Read
- Files.ReadWrite.All
- Group.Read.All
- Sites.Read.All
- TeamMember.Read.All
- User.ReadBasic.All
- User.Read (If not already added)
-
Scroll down to the bottom of the panel and click the Add permissions button
-
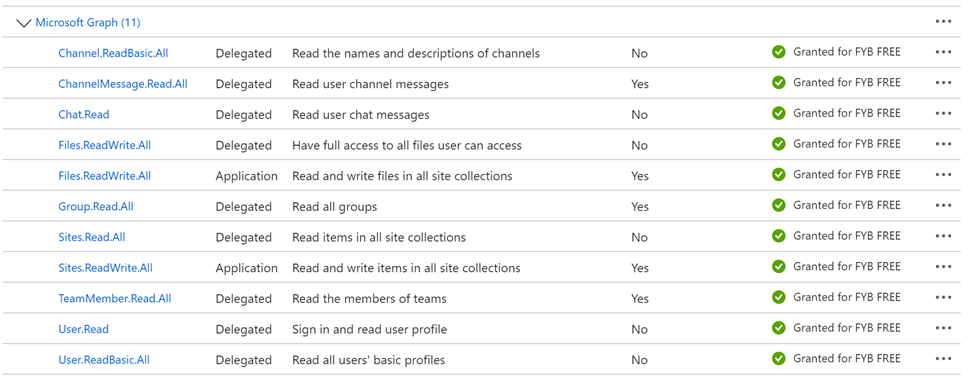
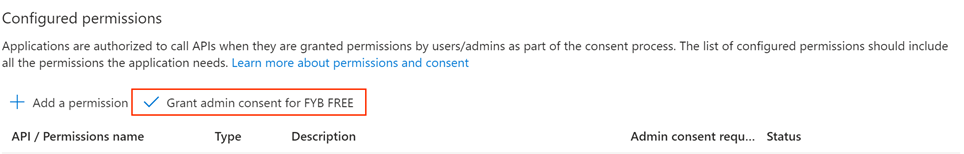
An Azure administrator will need to grant permission for the application to access the resources by clicking on the Grant Permission button
-
Once granted the status will update to Green, indicating the permission has been successfully granted
-
Click on Grant Admin Consent
 Note
Do not remove the default user.read delegated permission
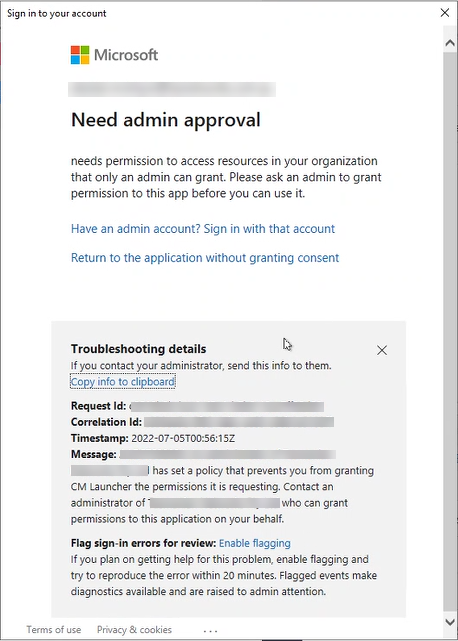
NoteNote if users are still receiving the below message upon the first login then an Azure Administrator will need to complete the first login and grant consent from the Microsoft login pop-up instead.
API PERMISSION USAGE
| NAME | TYPE | DESCRIPTION | CONSENT REQUIRED | USAGE |
|---|---|---|---|---|
| Channel.ReadBasic.All | Delegate | Read basic information from channels | Yes | Required for archiving all channel posts from a Team |
| ChannelMessages.Read.All | Delegate | Read all channel posts from a Teams channel | Yes | Required for archiving all channel posts from a Team |
| Chat.Read | Delegate | Read Personal Chat Messages | Yes | Required for archiving Teams Chats |
| Files.ReadWrite.All | Application | Read and write files in all site collections | Yes | This permission is used by the background scheduler to move documents from Sharepoint to Content Manager. |
| Files.ReadWrite.All | Delegate | Read and write files in all site collections | Yes | This permission is required for the Delete Document functionality in the 365 |
| Group.Read.All | Delegate | Read all groups | Yes | Required for showing a list of all Teams available for the organization and for archiving Teams Channel Posts |
| Group.Read.All | Application | Read all groups | Yes | Required for retrieving the names of members in a SharePoint site for the FYB Connect Access Controls functionality |
| Sites.Read.All | Application | Read and write items in all site collections | Yes | This permission is used to iterate over each site and library using the application permissions. This is required by the background scheduler to target specific sites so that the document can be moved across to Content Manager |
| Sites.Read.All | Delegated | Read items in all site collections | Yes | Used to display all sites that the logged in user has access to in the Sites page of 365|2CM |
| TeamMember.Read.All | Delegate | Get the number of members in a Teams | Yes | Required for generating Teams Channel post |
| User.Read | Delegate | Read basic information for logged in user | No | Default permission set by Azure, used to allow user to sign in |
| User.ReadBasic.All | Delegate | Gets the basic details of a 365 User | Yes | Required for retrieving the names of the Recipients in a personal Teams Chat |
| User.ReadBasic.All | Application | Gets the basic details of a 365 User | Yes | Required for retrieving the names of members in a SharePoint site for the FYB Connect Access Controls functionality |
EXPOSE THE API
Applying a custom scope to the registration will prevent unauthorized access to the 365|2CM API endpoints.
-
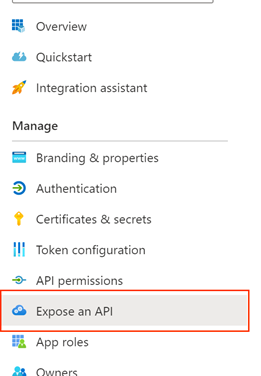
In the Left Menu, click on Expose an API
-
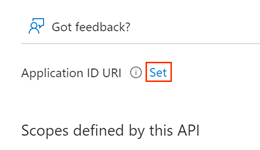
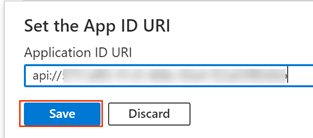
Next to the Application ID URI click on Set
-
Click Save
NoteDo not Change the Application ID URI. It must be in the following format: api://{client id}
-
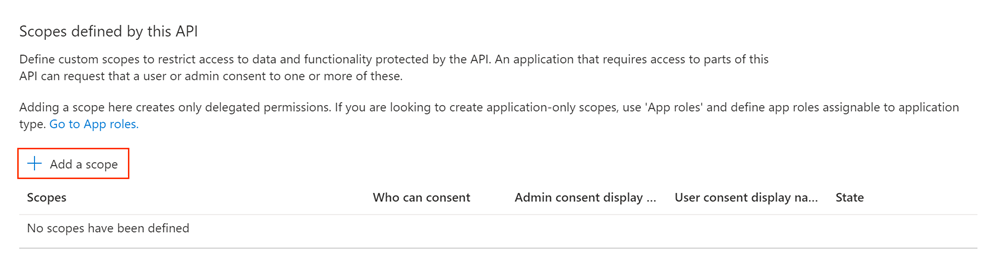
Click Add a scope
-
Specify the values below in the Add a scope window, then click Add scope
NoteThe scope must be named Grant.Access
Field Value Scope Name Grant.Access Who can consent? Admins and users Admin Consent display name Grant Access to 3652CM Admin consent description Grant Access to 3652CM State Enabled 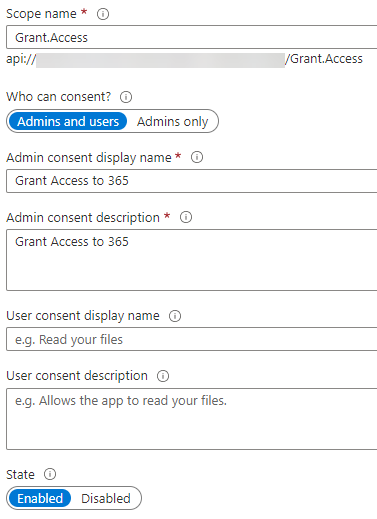
-
Once the scope has been added, click on API permissions
-
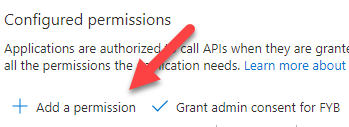
Click on Add a permission
-
Click My APIs

-
Click on the previously created 365|2CM Azure app registration
-
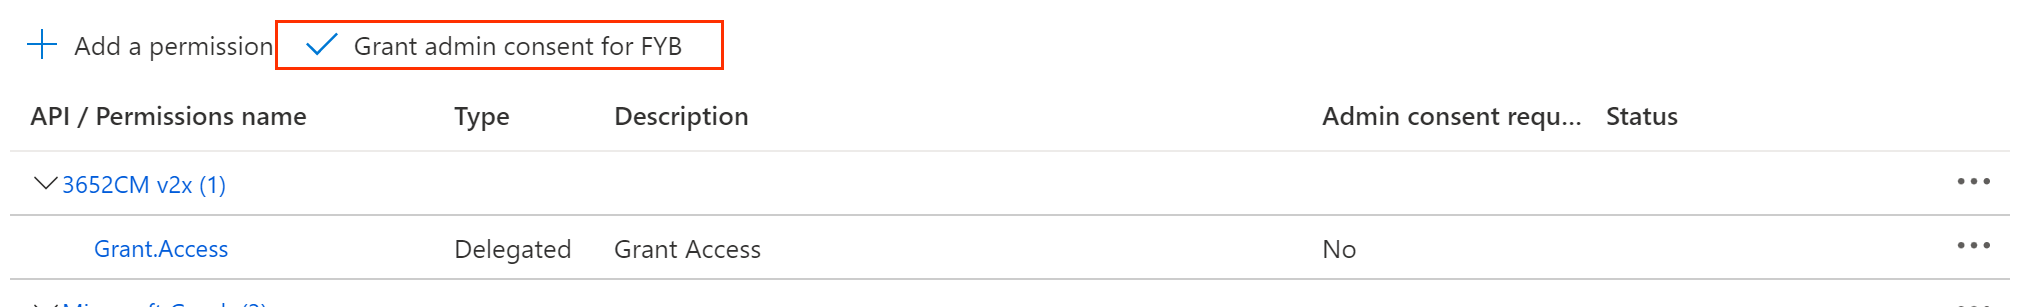
Click on the Grant.Access scope and then click Add permissions at the bottom of the screen

-
Click on Grant admin consent
GATHERING APP DETAILS
Please follow the steps below to retrieve the Application ID, Tenant ID and Redirect URL on the Azure portal. These values are required for the installation.
-
Once signed into the Azure portal click on Azure Active Directory
-
Click on App registrations

-
Click on the required application (365|2CM created previously)

-
Click on Overview
-
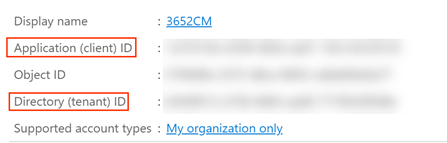
Copy the Application (client) ID and Directory (tenant) ID and note them down.
-
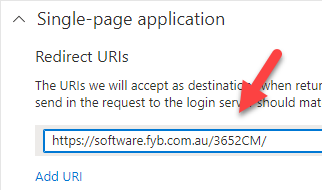
Click on Redirect URIs from the overview page

-
And then copy and note down the Redirect URI value
CERTIFICATE BASED AUTHENTICATION
The background scheduler component of the application utilizes certificate-based authentication to verify its identity to Microsoft Azure. As such you will need to register a certificate for your application on Azure AD. You can choose to use an existing certificate if you have one (the same certificate used for the 3652CM site) otherwise you can create/purchase a new certificate for this purpose. Please follow the steps below on how to upload a certificate:
-
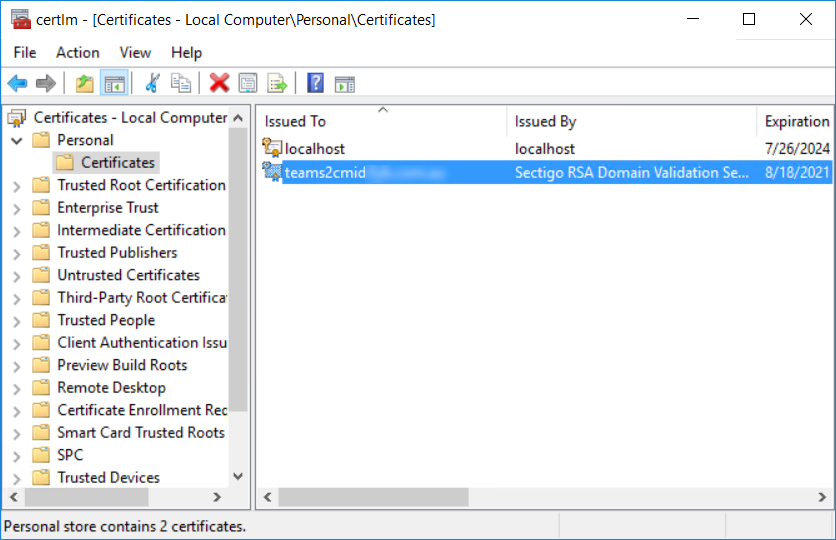
After obtaining a copy of your certificate (.pfx), install the certificate to the Certificate Manager tool under local machine on the server the application will be installed on
-
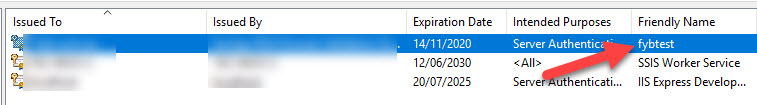
Ensure the certificate has been given a friendly name, this is required when installing the app to the server
-
Please ensure the account that will be running the application pool for the application has access to the certificate private key
-
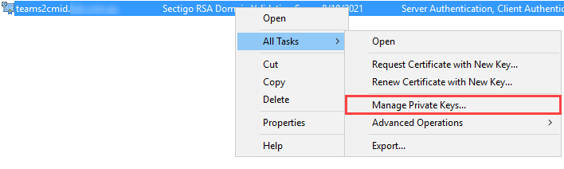
Right-click the certificate > All Task > Manage Private Key
-
Grant the account running the app pool full control permission on the certificate
-
Export the public key from the certificate using this guide (https://docs.microsoft.com/en-us/azure/application-gateway/certificates-for-backend-authentication), you will only need to complete steps 1 to 7 in the Export authentication certificate (for v1 SKU) section
-
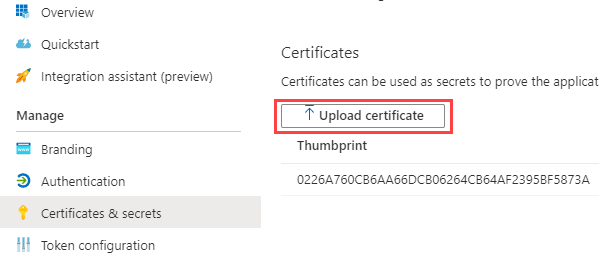
Upload your certificate public key (.CER) to Microsoft Azure for the 365|2CM application by going to the Certificates & secrets section
UPDATING THE CERTIFICATE FRIENDLY NAME
If the certificate in the Entra app has expired and the new certificate has a different friendly name, follow the steps below to update the certificate friendly name in FYB Connect:
-
Navigate to the 365|2CM install directory (C:\Program Files\FYB Pty Ltd\FYBConnect\3652CM)
-
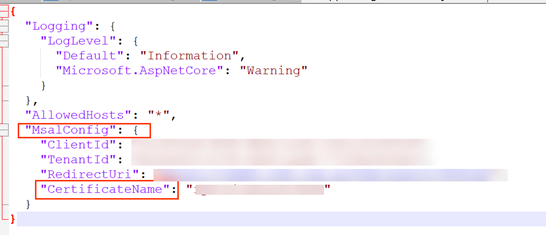
Open the appsettings.Production.json file as an Administrator
-
Within the MsalConfig section, update the value of the CertificateName property to the value of the new certificate friendly name
-
Save the file
-
Perform an app pool restart on the 365|2CM application within IIS
VALUES REQUIRED FOR INSTALLATION
The following values will be required for the installation of 365|2CM. Please ensure that the person responsible for the installation has these values.
- Redirect URI
- Application ID
- Tenant ID
- Certificate Friendly Name
| Name | Description |
|---|---|
| Redirect URI | The URI where Azure will send the authentication payload upon successful authentication. |
| Application ID | Application's unique identifier on AzureAD. |
| Tenant ID | The organization tenant's unique identifier on AzureAD. |
| Certificate Friendly Name | The friendly name of the nominated certificate (.pfx) installed on the machine. This certificate is used to prove the application's identity by encrypting the application's claims in the form of a JWT token. |
ENDPOINTS
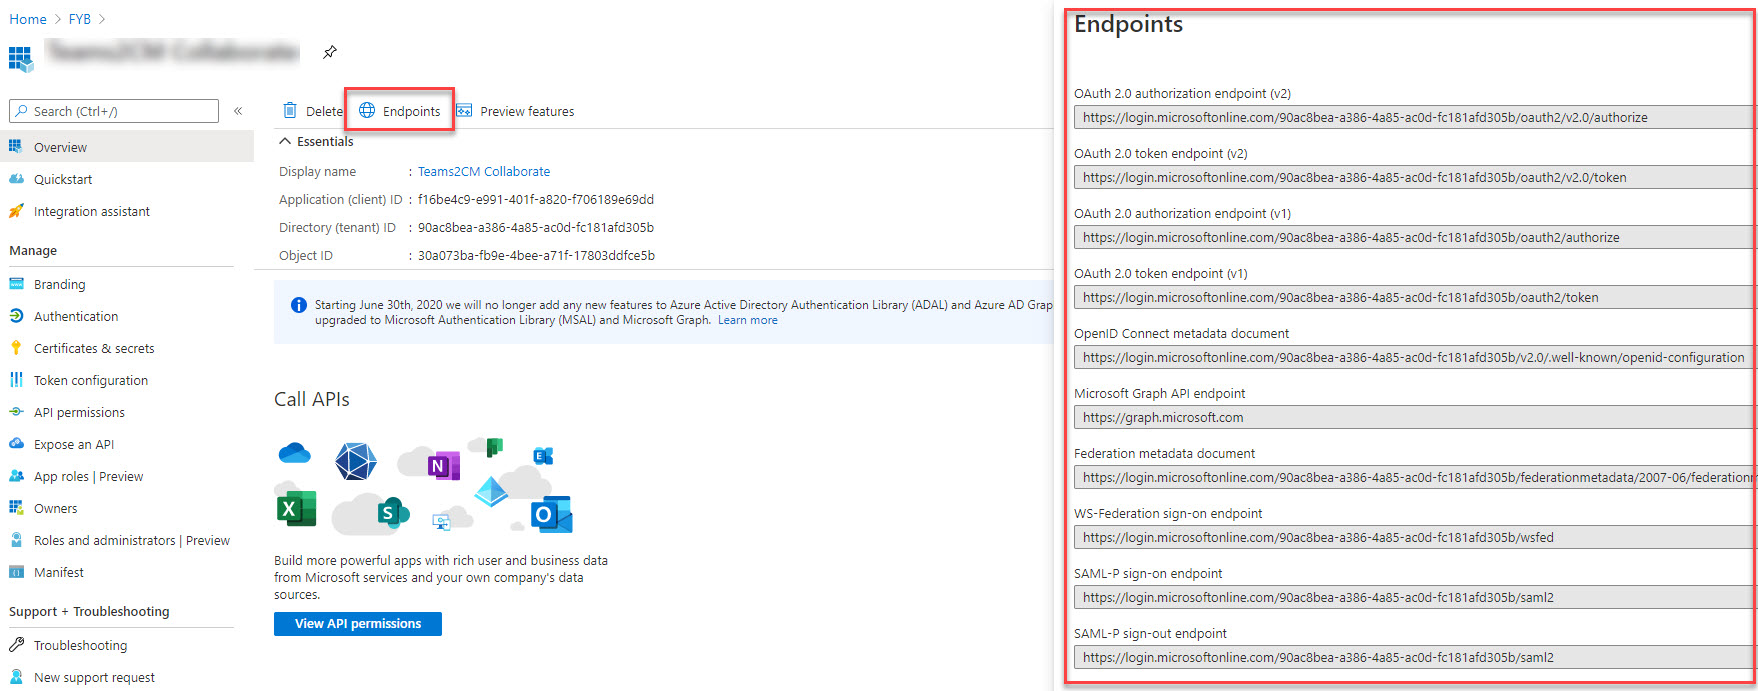
All valid endpoints for the registered application can be seen via the Azure web portal.
-
Select the registered application on Azure
-
From the Overview page select Endpoints